Bithumb Reports Data Breach as South Korea Reviews Financial Cyberattacks
The exchange is investigating whether customer information was exposed. It says the affected employee system is separate from its trading platform.
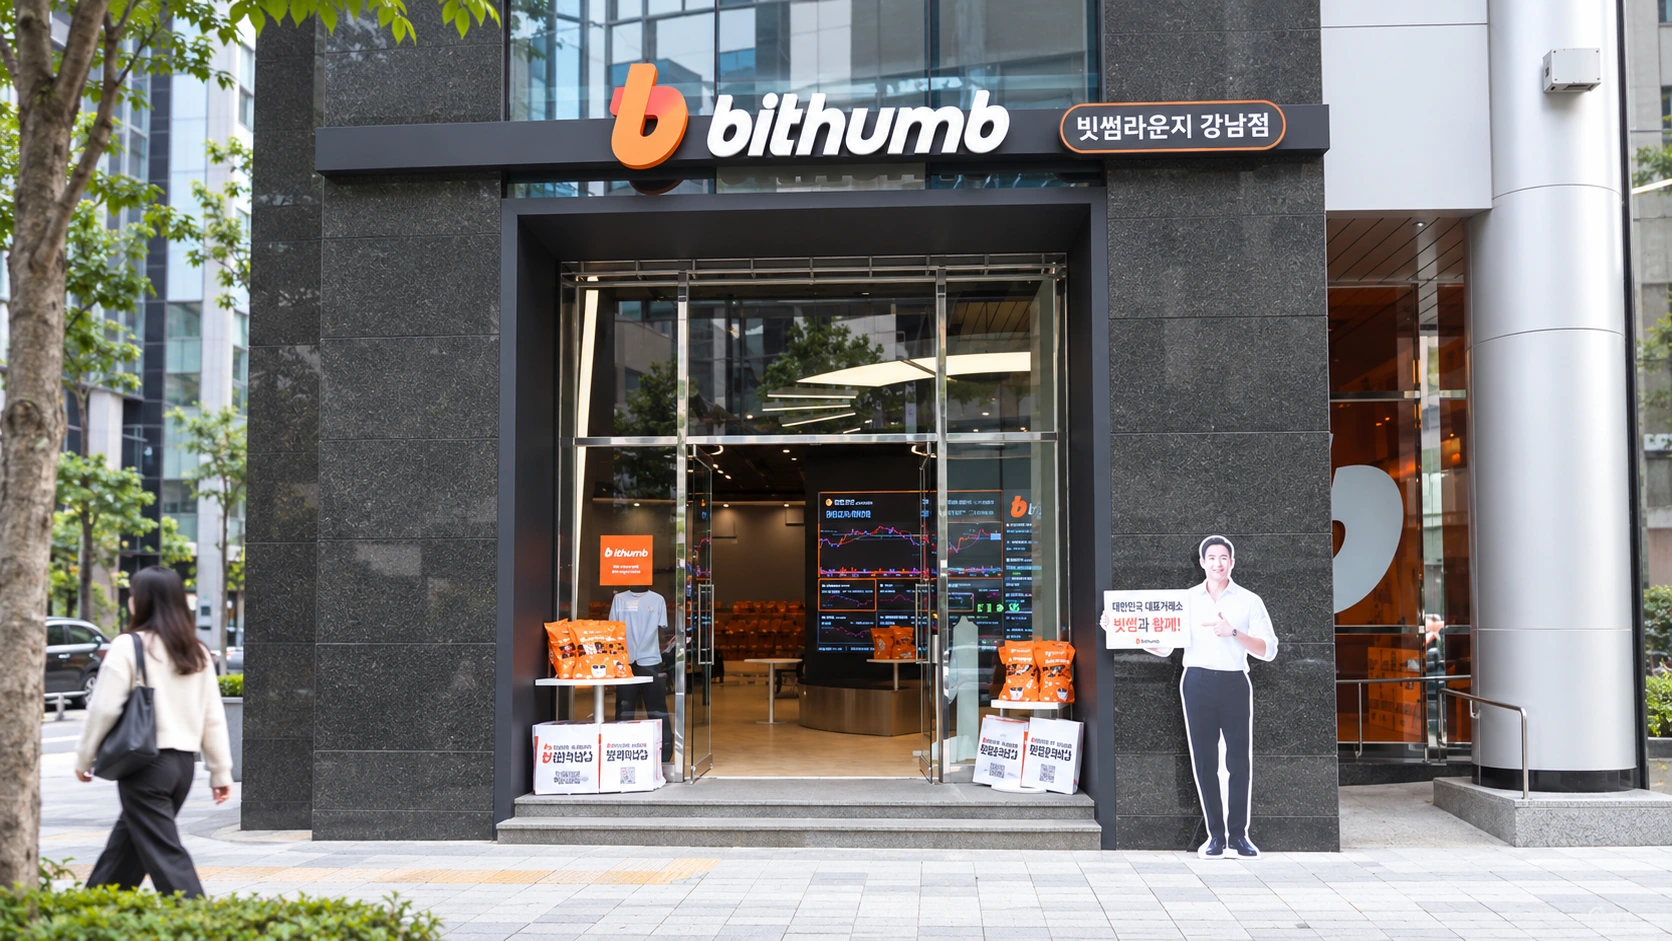
Bithumb reported a breach of an internal employee system on Wednesday as South Korean authorities reviewed cyberattacks affecting several financial firms. The cryptocurrency exchange was investigating the scope of a personal-information leak, including whether member information was involved. The public reports did not establish how many Bithumb users were affected or identify a confirmed theft of customer cryptoassets.
According to SBS, the exchange detected unauthorized access to its internal mobile groupware system on Tuesday and reported the incident to the Korea Internet & Security Agency and the Personal Information Protection Commission. Groupware is software employees use for work and communication. The breach concerns that internal environment, rather than a disclosed exploit in a public blockchain.
The distinction is central to understanding the incident. A centralized exchange operates trading, customer-service, identity and employee systems alongside its asset custody arrangements. A compromise of one system can be serious without proving that every other system was accessed. TTN's coverage of a separate wallet-security update illustrates why identifying the affected component matters before drawing conclusions about funds.
The exchange's assurance has a defined scope
CoinDesk reported Bithumb's statement that the compromised system is separate from its trading platform and cannot be used to access customer virtual assets. That is the exchange's account of the system boundary, rather than an independently published forensic finding. Its investigation into possible member-data exposure was still continuing in the reports reviewed for this article.
The exchange had not disclosed a count of affected people or said whether deposits and withdrawals were disrupted, according to CoinDesk. Those unanswered points should remain distinct. A missing operational update is not evidence that transfers were suspended, just as an assurance about assets does not establish that no personal information was exposed.
For users, the significance of a data breach extends beyond an immediate account balance. Contact information can help a fraudster construct a convincing impersonation attempt. That risk does not require possession of a customer's cryptoassets. Claims about stolen funds, leaked credentials and exposed personal records therefore need separate evidence; they cannot be substituted for one another in describing the incident.
Other firms reported separate incidents
Yonhap reported that Daishin Securities said personal information belonging to 38,490 customers had been leaked. The number belongs to Daishin, not Bithumb. The brokerage described names, email addresses and mobile-phone numbers among the information affected, and said it was investigating with authorities and notifying customers. Applying that figure to the exchange would materially overstate what is known.
Mirae Asset Global Investments also reported abnormal access to some web systems. SBS reported the company's statement that it blocked the access route and activated an emergency response, with the information involved understood to relate to certain administrative systems rather than retail-investor records. The firms' descriptions concern different environments and should not be merged into a single confirmed technical attack.
The incidents nevertheless created a broader financial-sector concern. Yonhap reported that the presidential office held an emergency meeting on Wednesday involving financial, science, privacy and cybersecurity officials. The discussions covered the investigations, information sharing and measures to prevent phishing using leaked personal information. The report described a coordinated government response, not proof that the separate intrusions had the same attacker.
The next evidence needs to identify exposure and impact
For Bithumb, a substantive update would specify which records were accessed, the number of affected people and any consequences for account operations. Technical findings about the entry point and the separation of systems would help readers evaluate the exchange's initial assurance. None of those details can be inferred simply from a change in cryptocurrency market prices.
There is also a difference between an unauthorized asset transfer and a privacy incident. Our report on CoinDCX's separate wallet loss concerns a disclosed asset-loss mechanism. Bithumb's current report concerns access to an employee system and unresolved data exposure. Keeping those categories precise allows readers to assess the actual development without treating every crypto-related security headline as evidence of the same failure.
Sources and methodology
Sources checked October 28, 2026. Company statements and reported findings are attributed in the text. Explanations of financial and operational implications are TTN editorial analysis.
- SBS: Bithumb intrusion, discovery date and regulator notifications
- CoinDesk: exchange statement on trading-system separation and unresolved questions
- Yonhap: separate breaches at financial firms and Daishin customer count
- SBS: distinct company accounts of the incidents
- Yonhap: presidential-office emergency meeting and phishing response